HOME
MY PAGE


イベントトップに戻る
セミナースケジュール
Dec.9_10:30_サイバーセキュリティフォーラム
サイバーセキュリティフォーラム
半導体業界のサイバーセキュリティ強化に関する最新の取り組みを一挙紹介
2026/12/9(水) | 10:30 - 13:00
 会議棟 605-606会議室
 日英翻訳サポートをご利用希望の方
ご自身のスマートフォンおよびイヤホンをご持参ください。
※詳細はFAQをご確認ください。
インシデント対応から得られた教訓を今後の対策に生かす取り組みや、脅威ハンティングなどのプロアクティブなセキュリティアプローチ、さらにEU CRAやSEMI E187 Version 2をはじめとする法制度・業界標準の最新動向など、半導体業界のサイバーセキュリティの今をお伝えします。
※プログラムは都合により変更となる場合がございます。予めご了承ください。
プログラムアジェンダ
萩尾 英二(東京エレクトロン)
概要文が入ります。
サイバー攻撃の高度化・巧妙化が進む中、企業にはインシデントの発生を想定した実効性のある対応力が求められています。しかし、実際のインシデント対応では、技術的な対処だけでなく、状況把握や意思決定、関係部門との連携、事業への影響を踏まえた判断など、さまざまな課題に直面します。 本講演では、実際のインシデント対応の経験をもとに、対応の過程で直面した課題や苦労、そこから得られた教訓を紹介します。 また、これらの経験を踏まえ、被害の拡大防止や迅速な復旧に向けて何を準備すべきか、今後求められるセキュリティ対策と組織の対応力について考えます。
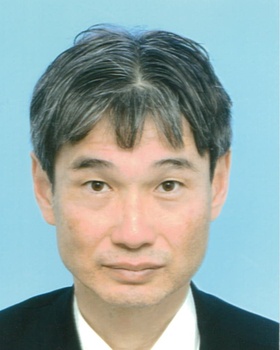
巧妙化・高度化するサイバー攻撃は、既存のセキュリティ対策での対応が困難なため、侵入を前提に侵害痕跡を探索する脅威ハンティングが必要である。本発表では、脅威ハンティングの概要等を紹介するほか、今夏のサイバーセキュリティ戦略本部で決定された「脅威ハンティングの普及組織、実施等に係る基本方針」と関連施策について説明する。
概要文が入ります。
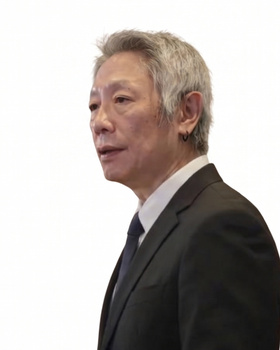
SEMI E187, Specification for Cybersecurity of Fab Equipment, was first published in January 2022 to establish fundamental cybersecurity requirements for semiconductor manufacturing equipment. The standard provides a common security baseline covering operating system security, network security, endpoint protection, and security monitoring, helping equipment suppliers and semiconductor manufacturers reduce cybersecurity risks throughout equipment deployment and operation. As semiconductor manufacturing environments become increasingly connected and cyber threats continue to evolve, the industry faces new challenges involving legacy systems, equipment lifecycle management, remote access, and varying security requirements across different equipment types. These challenges have driven the development of SEMI E187 Version 2, a major revision designed to enhance the standard's applicability, flexibility, and alignment with evolving industry security needs. This session will provide an overview of SEMI E187's background and objectives, explain the key drivers behind the Version 2 revision, and introduce the proposed improvements, including risk-based security levels, expanded equipment coverage, enhanced technical security requirements, and stronger alignment with international cybersecurity standards such as IEC 62443. The presentation will also highlight the current revision status, ongoing industry collaboration, and the expected benefits for semiconductor equipment suppliers and manufacturers in strengthening cybersecurity resilience across the semiconductor manufacturing ecosystem.
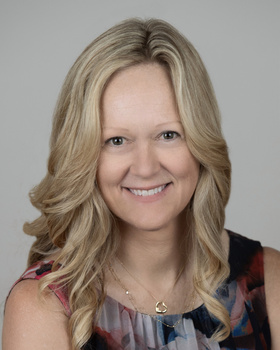
Cybersecurity is no longer simply an IT issue. For the semiconductor industry, it has become a critical element of manufacturing resilience, supply-chain security, and the ability to reliably deliver the technologies on which our increasingly connected world depends. The semiconductor ecosystem is uniquely complex and interconnected, spanning equipment, materials, devices, software, manufacturing, and an extensive global supply chain. As a result, no single company can address cybersecurity challenges alone. Protecting our industry requires collaboration across organizational and geographic boundaries, greater sharing of expertise and best practices, and the development of common approaches that strengthen trust throughout the ecosystem. Forums such as this provide an important opportunity to exchange knowledge and identify emerging challenges, but the real impact comes from what happens next. By taking these insights back into our organizations and continuing to collaborate through SEMI, we can move from discussion to action and collectively build a more secure, resilient, and trusted semiconductor industry.